Website basics
Understand what HTTPS protects
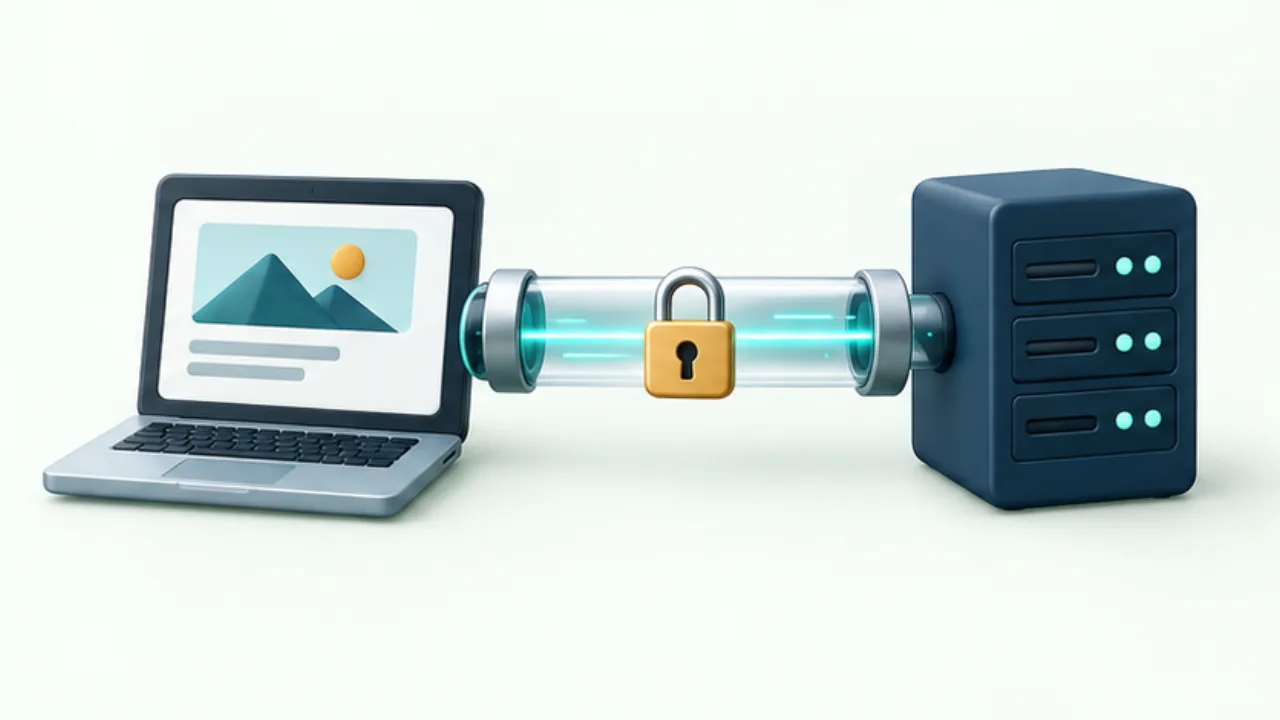
HTTPS protects communication between the browser and server. It does not by itself establish the trustworthiness of the site's content or operator.
On this page
Understand the transport protection
HTTPS uses TLS to encrypt communication and protect it against interception and modification in transit. It does not determine how the recipient handles submitted data.
Read the destination name
A lookalike domain can also use HTTPS. Inspect the hostname and whether it is the intended recipient before entering information.
Check resources as an operator
Inspect images and scripts that still use HTTP addresses. Mixed content on an HTTPS page may be restricted by the browser.
Resolve warnings rather than bypassing them
Check certificate validity, covered names, and hosting configuration. Do not count a page reached by ignoring a certificate warning as a successful publication test. Record the warning, URL, and time for diagnosis.
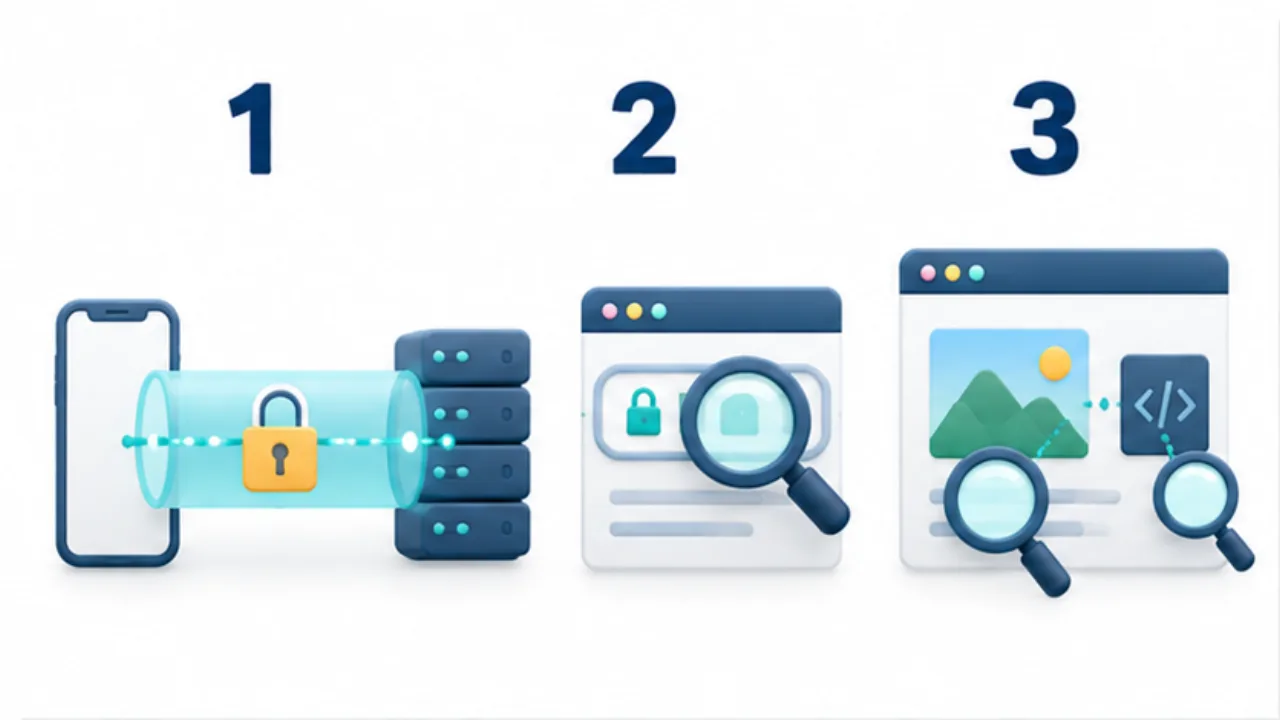
Select the image to enlarge.
- HTTPS protects communication between the endpoint and server.
- Check that the hostname identifies the intended recipient.
- On your own site, inspect where images and other resources load from.
Distinguish the protected connection from correct information
HTTPS describes protection during communication. Whether a document is accurate, an operator is the expected business, or submitted information is handled appropriately remains a separate question.
As a visitor, inspect the actual destination hostname rather than only the link's label. As an operator, verify the exact name you publish to visitors. Similar-looking aliases still require their own configuration checks.
Example: the page loads but images are missing
Suppose a newly published page shows text while some images or functions are absent. Record the page URL separately from the failing resource addresses.
Inspect whether older HTTP references remain and whether browser diagnostic messages identify a problem. Do not classify every missing image as mixed content: a missing file or incorrect path is another possibility.
Match an observed warning to the actual reference, correct the identified issue, and review other pages using the same resource. This turns a vague visual symptom into a specific investigation.
Organize the publication review
| Perspective | What to verify |
|---|---|
| Name | Published hostname and actual destination |
| Connection | No unresolved certificate or connection warning |
| Page resources | Required images, scripts, and other references |
| Content | Correct explanation and contact information |
The content row is outside HTTPS's own function, but it still belongs to reviewing the public site. If a form collects information, also compare its intended recipient with the implementation.
Do not make bypassing a warning part of the normal acceptance procedure. Resolve the relevant condition, then repeat the affected check.
For a handoff, include the URL and warning text along with any screenshot. That gives the next person the exact endpoint and symptom to inspect. A working protected connection is a necessary technical result; the wider publication review establishes whether the page actually communicates and behaves as intended.